For engineering and compliance leads at EU software manufacturers
Your product falls under the CRA. Your customers fall under NIS2.
Can you prove what shipped in your last release?
Since 11 September 2026, CRA Article 14 obliges manufacturers to report actively exploited vulnerabilities. From 11 December 2027, Annex I adds a machine-readable SBOM for every product. Your NIS2-regulated customers are already asking for the same evidence in supplier questionnaires. Eurtifact produces that evidence chain, per release.
Not an official EU institution. Eurtifact provides technical controls aligned with EU regulations.
How It Works
The Digital Customs House
Every artifact follows the same controlled path from untrusted source to verified distribution.
Upstream Sources
Monitors public registries (Docker Hub, GHCR, Quay) for images on your allowlist. New versions and tags are detected automatically.
Quarantine & Mirror
Pulls each artifact into an isolated quarantine project. Nothing is accessible to tenants until inspection is complete.
Scan & Certify
Known CVEs are scanned for. CycloneDX SBOMs are generated. Cosign signatures are applied. Each step is recorded as a lifecycle event.
Policy Gate
Tenant-defined admission policies determine what gets promoted. The platform enforces data completeness. Each organisation sets their own thresholds.
Secure Distribution
Approved artifacts are distributed to tenant registries within EU jurisdiction. Every pull is logged. Full traceability from source to deployment.
Built for EU Software Manufacturers
NIS2 Aligned
Active in Germany since December 2025, affecting ~29,500 organisations. Provides technical controls aligned with NIS2 Article 21(2): incident handling, supply chain risk management, vulnerability disclosure, and cryptographic verification.
AlignedCRA Aligned
Addresses CRA Annex I Part II requirements: vulnerability lifecycle management, machine-readable SBOMs, secure update distribution, and structured incident reporting per Article 14.
AlignedGDPR Aligned
Zero personal data in artifact operations. Pseudonymised audit logs, EU-only data processing, and data minimisation by design per GDPR Article 32.
AlignedEU Data Sovereignty
All primary infrastructure hosted in EU data centers (Hetzner, Nuremberg, Germany). BSI-supervised hosting provider. Compute, storage, and backups remain within EU jurisdiction.
EU-OnlyThe Regulatory Landscape
Regulation Mapping
How Eurtifact's technical controls align with EU regulatory requirements.
Network and Information Security Directive 2 (EU 2022/2555)
Active Now| Reference | Requirement | Platform Control |
|---|---|---|
| Art. 21(2)(a) | Risk analysis | Per-tenant policy engine, vulnerability posture assessment |
| Art. 21(2)(b) | Incident handling | Structured reporting with configurable notification windows |
| Art. 21(2)(d) | Supply chain security | Allowlist-based curation, upstream provenance tracking |
| Art. 21(2)(e) | Secure development | Quarantine-scan-certify pipeline, immutable build records |
| Art. 21(2)(h) | Cryptography | Artifact signing (Cosign), TLS 1.3 in transit, AES-256 at rest |
Cyber Resilience Act (EU 2024/2847)
Reporting Active| Reference | Requirement | Platform Control |
|---|---|---|
| Annex I Part II(1) | SBOM in machine-readable format | CycloneDX generation for every artifact version |
| Annex I Part II(2)-(3) | Vulnerability remediation and testing | Automated vulnerability scanning, lifecycle state tracking |
| Annex I Part II(5) | Coordinated vulnerability disclosure | security.txt (RFC 9116), SECURITY.md |
| Annex I Part II(7) | Secure update distribution | Signed artifact distribution to tenant registries |
| Annex I Part I | Secure by design properties | Quarantine-first architecture, hash-chained audit trail |
| Art. 14 | Incident reporting to CSIRT/ENISA | Structured incident workflow with configurable timelines |
Eurtifact is a managed platform. Each organisation receives a dedicated tenant with isolated policy controls and audit trails. Hosted in EU (Hetzner, Germany).
Built on CNCF-graduated and industry-standard open-source components.
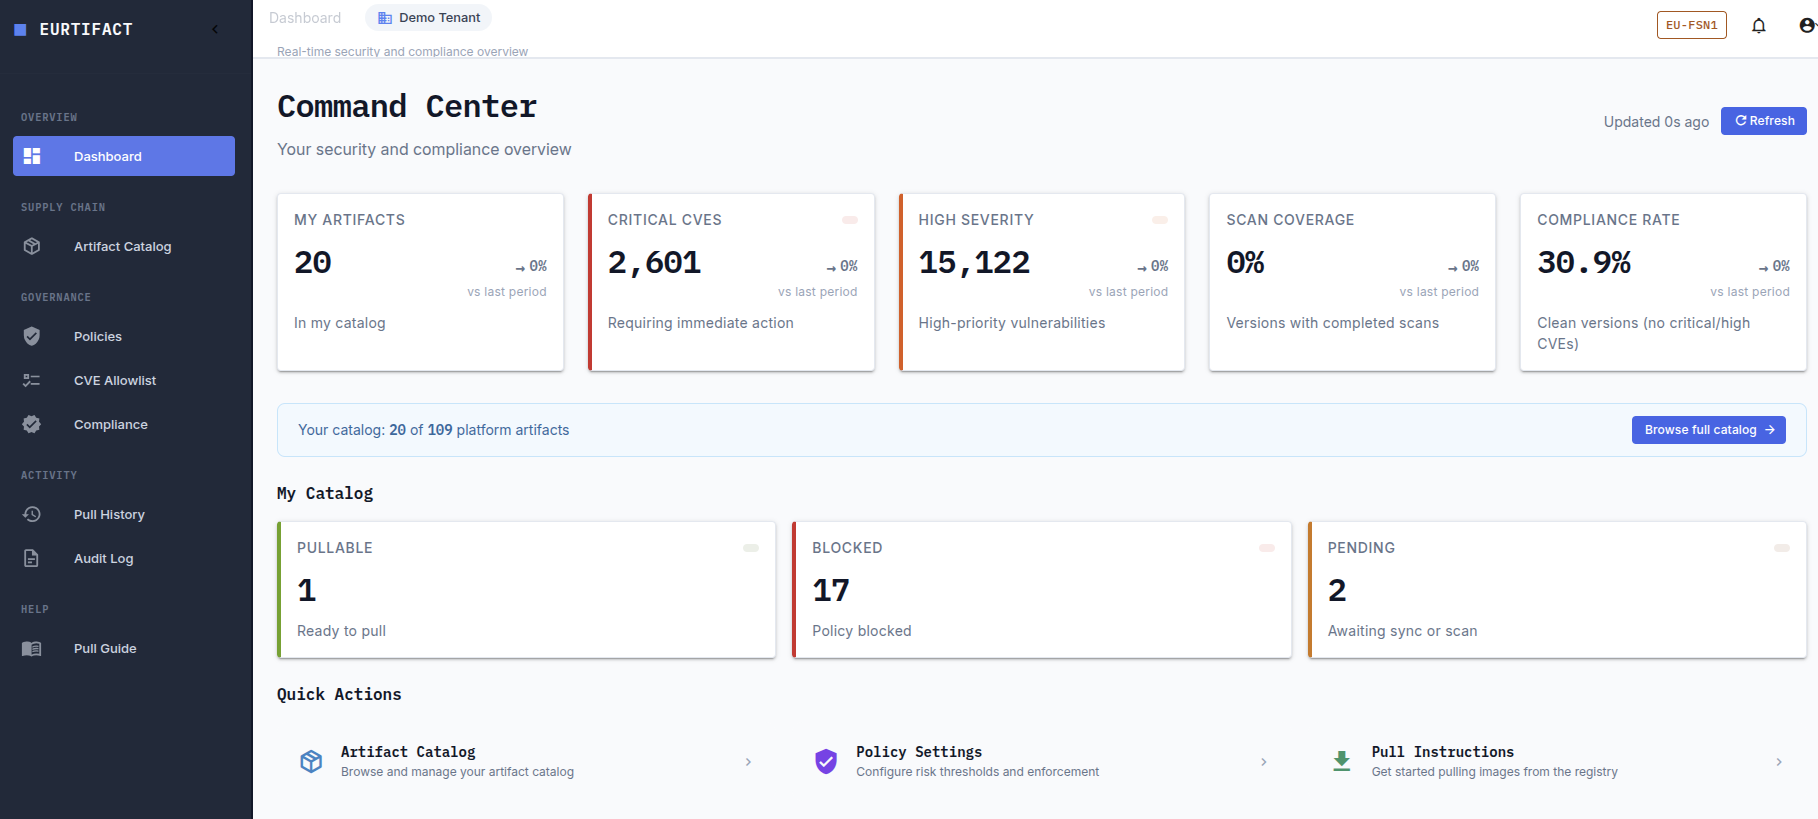
See the Platform
Real views from a live Eurtifact tenant.
NIS2 obligations are active.
CRA Art. 14 reporting: binding since 11 September 2026.
See how Eurtifact provides the tamper-evident audit trail that NIS2 and CRA auditors need — automated scanning, compliance reporting, and guaranteed EU data sovereignty.
Or reach us directly at sales@eurtifact.eu